
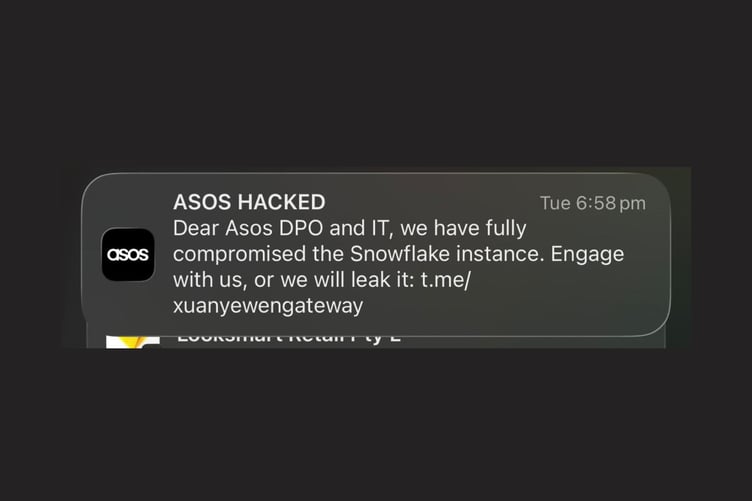
I received an unexpected notification from the ASOS app on my phone earlier this week.
For many residents in the island, ASOS is a familiar online shopping destination, offering a wide range of clothing and beauty products that may not always be available in local shops.
But this notification was not about a new collection or a sale.
It read: ‘Dear ASOS DPO and IT, we have fully compromised the Snowflake instance. Engage with us, or we will leak it: t.me/xuanyewengateway.’
‘Hmm, that’s strange,’ I thought.
In all honesty, I initially assumed it was some kind of marketing technique.
Clicking on the link took me straight to the ASOS sale page. ‘Cheeky,’ I thought, before having a browse anyway.
The message, however, was part of an apparent attempt at extortion targeting the retailer.
ASOS, which stands for ‘As Seen On Screen’, is a British online fashion and beauty retailer serving customers around the world.
Following reports of the incident, I discovered that the situation appeared more serious than I had initially thought.
ASOS had contacted customers on Tuesday, October 6, although they must have forgotten about me as I am yet to receive an email.
Entering full investigative mode, I returned to the crime scene and opened the app, asking to speak to someone about the incident through their online chatbot.
I explained that I had not received any information about the reported hack and data breach.
The automated response arrived almost instantly, apologising for the unauthorised notification and any uncertainty it had caused.
It stressed that protecting customers remained a priority and that an investigation involving internal and external cyber security experts was under way.
In the automated message I received, ASOS confirmed that some personal information had been accessed, including names, contact details and certain non-personal account-related information.
It went on to state: ‘Since we began our internal investigation, we have found that no payment card information or account passwords were accessed.’
I was also reassured that the app remained safe to use.
Then I was connected to a customer service agent, who provided further information about how the incident had occurred.
ASOS said an unauthorised party had gained access to an employee account after impersonating a trusted contact to obtain login credentials. These credentials were then used to access information on certain third-party platforms used by the company.
The affected platforms were secured, and an investigation was launched with support from cyber security experts, law enforcement and regulatory authorities. ASOS also said it had taken additional steps to strengthen its security controls.
I was not the only customer concerned about the incident.
Manxman Ben Peberdy, who now lives in Australia, was also affected by the hack.
He said: ‘I was worried that my personal information and banking details would get taken, especially because I had just done an order from there.’
So, should customers consider the matter closed?
While ASOS has reassured customers that payment information and passwords were not accessed, the incident highlights the risks posed by cybercriminals exploiting trusted relationships to gain access to company systems.
ASOS has advised customers with concerns to contact its customer service team.
As a precaution, I have changed my password through the app and removed my saved card details.
I may have fallen at the first hurdle, but I'll certainly be keeping my eyes peeled for any future cyber tricks.